Skip to content
-
Security You Can Trust, Expertise You Can Rely On. TekGenX Consulting

NetwerkLABS

Powered By TEKGENX CONSULTING

  • ATTACK
    • PenTest
    • Web Pentest
    • C2 Frameworks
    • VulnLAB
  • DETECT
    • Detection Engineering
    • DFIR
    • EDR | SIEM | SOAR
    • Purple Teaming
    • MITRE ATT&CK
  • DEFEND
    • CTEM
    • Attack Surface Management (ASM)
    • Network Infrastructure
    • Vulnerability Management
    • WAF | Firewalls | IDS/IPS
  • LEARNING PATHS
    • Wazuh SIEM & XDR
    • Attack & Defend AD
    • Cheat Sheets
  • GRC
    • ISO/IEC 27001
    • NIS2 | CyFUN
    • NIST
    • CIS Controls
  • CTI
    • Threat Intel
    • CyBER-NEWS
Subscribe
Top Stories
Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: II]
8 LOLBins Every Threat Hunter Should Know
Living Off the Land (LOTL) Resources
Volatility3: Memory Forensics Cheatsheet
Misbehaving binaries: Hunting LOLBinsĀ 
Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: I]
Testing Your Defences: TTP Simulation with Atomic Red Team
Stakeholder-Specific Vulnerability Categorization
NIS2 to ISO 27001:2022 Mapping Table
NetBox Labs: Bringing Clarity and Control to Modern Network Infrastructure
CyFUN Implementation: A Practical Roadmap
XSS vs SSRF: Two Different Trust Boundaries, Two Different Attacks
Importing the Wazuh 5.0 Beta OVA into Proxmox
Exploring Wazuh: Introduction
NIS2: A Complete Article-by-Article Reference
Metasploit: Quick Reference Sheet
HAVOC C2: COMMAND & CONTROL FRAMEWORK [PART – I]
Wireshark Threat Hunting – From Packets to Indicators [HTTP: DEEP-DIVE]
SETUP DVWA ON WINDOWS
Wireshark Threat Hunting – From Packets to Indicators [SMB: DEEP-DIVE]
Wireshark Threat Hunting – From Packets to Indicators
Nmap Cheat Sheet
ISO 27001 Annex A Controls: A Practitioner’s Guide to the 93 Controls
Atomic Red Team — Adversary Simulation and Detection
The Bait Lab – Phishing Simulations, Practical Campaigns with GoPhish & Evilginx (PART: II)
The Bait Lab – Phishing Simulations, Practical Campaigns with GoPhish & Evilginx (PART: I)
RED Teaming: Mythic C2 Framework
Installing OpenBAS: The OpenSource Breach and Attack Simulation
Metasploit Framework (MSFconsole) Cheatsheet
OpenCTI – Open Source Threat Intelligence Platform: PART I
SIEM: Onboarding WIndows Servers
Command & Control Mastery with Covenant C2: PART-I
Active Directory Enumeration with PowerView
TryHackMe: PyRAT
Install Docker on ParrotOS
Hunting the hunters: DFIR with Velociraptor (PART-II)
Hunting the hunters: DFIR with Velociraptor (PART-I)
Caldera: Simulating a Complete Attack Chain
Installing Caldera on ParrotOS: A Smoother Experience Compared to Ubuntu and Kali Linux
Vulnerability Management: FARADAY
Atomic Red Team – A Framework for Threat Emulation: PART II
Atomic Red Team – A Framework for Threat Emulation: PART I
Data Manipulation in Splunk: PART II
Data Manipulation in Splunk: PART I
Regular Expressions
Active Directory Domain Service (AD DS)
GRC 101: SimpleRisk Core (Community Edition)
Metasploit Cheat Sheet
Shodan 101
Wireshark 101 | Traffic Analysis and Investigation (PART 04)
Wireshark 101 | Traffic Analysis and Investigation (PART 03)
Concepts of Forensic Imaging
Wireshark 101 | Traffic Analysis and Investigation (PART 02)
Wireshark 101 | Traffic Analysis and Investigation (PART 01)
Endpoint Detection and Response (EDR) : Lima Charlie (Part 01)
SNORT 101 (Part 03)
SNORT 101 (Part 02)
Snort 101 (Part 01)
Splunk SIEM: Search Processing Language (SPL) Basics
Ā Ship OPNSense Firewall Logs ToĀ Splunk SIEM
Wazuh: VirusTotal Integration
Operationalizing Security: CALDERA Meets WAZUH (PART II)
Operationalizing Security: CALDERA Meets WAZUH (PART I)
(TryHackMe) Servidae: Log Analysis in ELK
TD_003
Threat Detection Engineering
Log Analysis: Basics
Splunk SIEM: Exploring SPL
Threat Intelligence with MISP: Part 1 – Setting up MISP with Docker
Thraet_Detect_TWO
Useful Windows Event IDs
Yara
Web Attacks
close up view of system hacking
NIST Cybersecurity Framework (CSF) and ISO/IEC 27001
close up view of system hacking
Digital Operational Resilience Act (DORA)
Test Page
CTI_June2024: Multiple Vulnerabilities in Google Chrome Could Allow for Arbitrary Code Execution
Wazuh: Detecting Web Attacks
Ingesting OPNsense logs into Wazuh SIEM
THREAT EMULATION: Introduction
Decoding
IR_002
Code Obfuscation and Deobfuscation
Incident Response
Remote Monitoring and Management software used in phishing attacks
Pyramid of Pain
MISP (Malware Information Sharing Platform)
SOC Home LAB: Elastic SIEM Installation
Incident Report Template
Windows Event Logs
Wireshark 101 | Packet Operations
SOC Tools and Useful Links
ELASTIC SIEM: KibanaĀ Query Language (KQL)Ā 
MITRE Framework
GOAD v2 Installation
DFIR: Core Windows Processes
Remotely Upgrading Wazuh Agents – CLI Method
L4 – L7 Load Balancing
BIG-IP LTM: Deployment Models
BIG-IP LTM: Load Balancing Methods
Threat Intelligence for SOC
Threat Detection: Detecting a Webserver Attack
Detection Engineering vs Threat Hunting
Posted inThreat Hunting DETECT MITRE ATT&CK

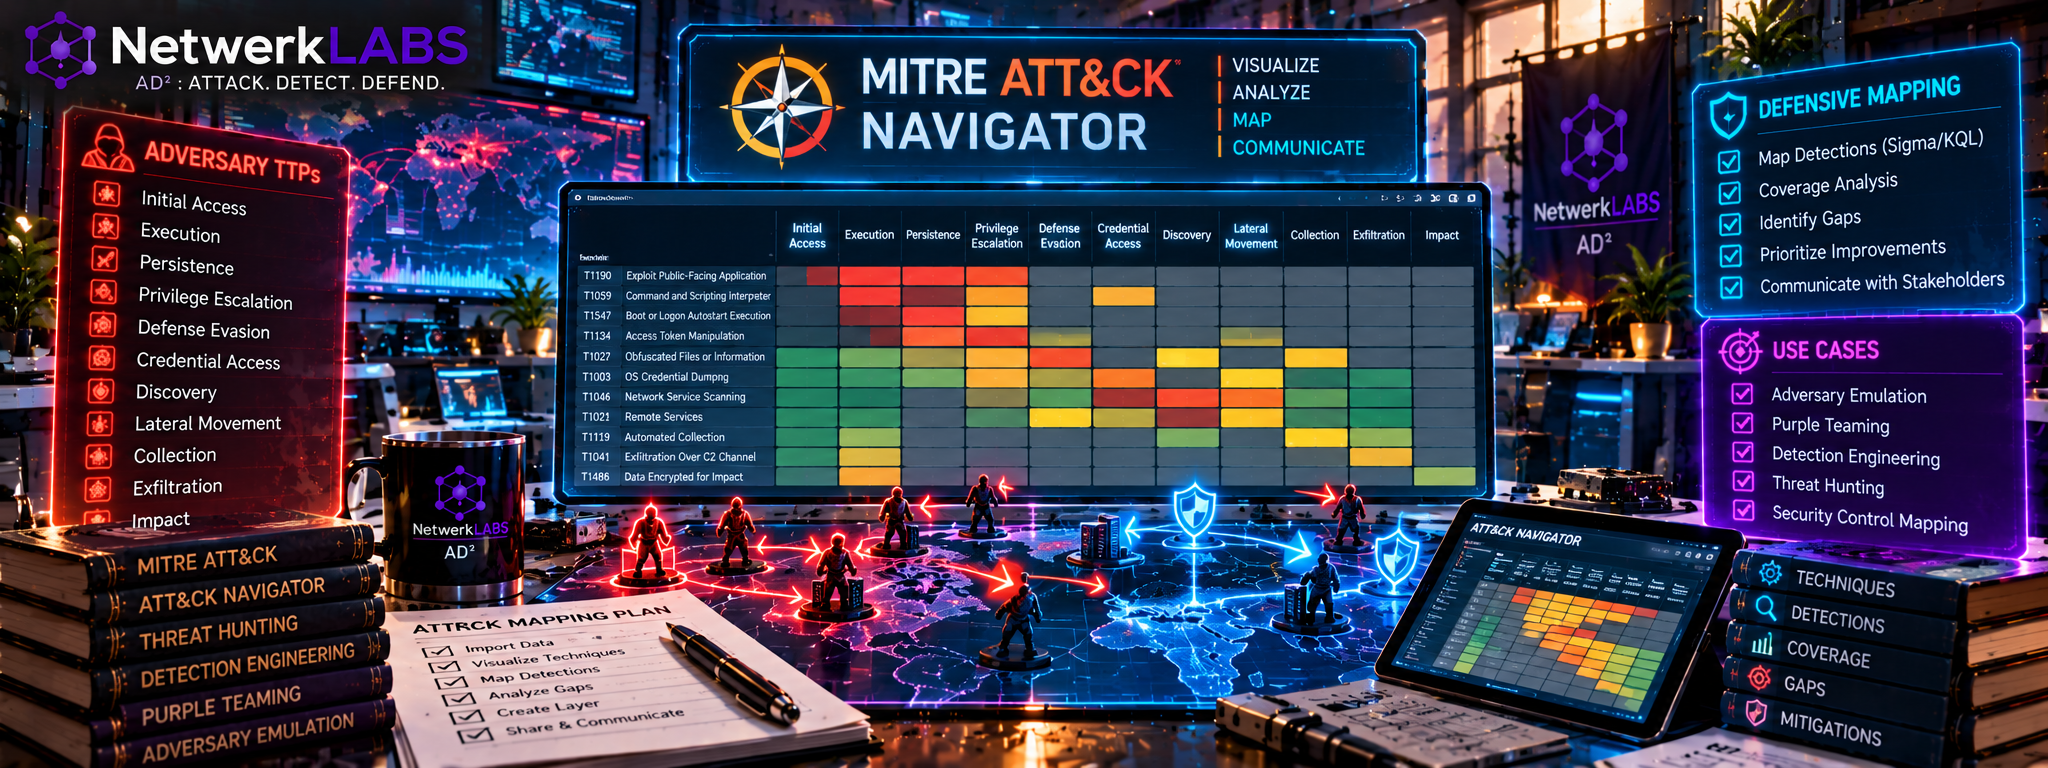
Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: II]

šŸŽÆ A Hands-On, Step-by-Step Walkthrough šŸ“š 1. Why Map a Threat Group at All? A threat model that stops at "we might get hacked" is not much use. ATT&CK lets you say something far more specific:…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
Posted inThreat Hunting DETECT Detection Engineering

8 LOLBins Every Threat Hunter Should Know

šŸ•µļøā€ā™‚ļø 8 Key LOLBins and Hunting Them with Elastic Security šŸŽÆ Attackers love tools that are already installed, already signed and already trusted. This post walks through the eight Windows binaries that showed up most often…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
Posted inATTACK Detection Engineering DETECT

Living Off the Land (LOTL) Resources

🌿 Living Off the Land (LOTL) Resources šŸ—ŗļø šŸŽÆ Attackers don't always bring their own tools. Sometimes the best weapon is already sitting on the machine. This guide walks through a well-organized collection of Living Off…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
Posted inDFIR DETECT

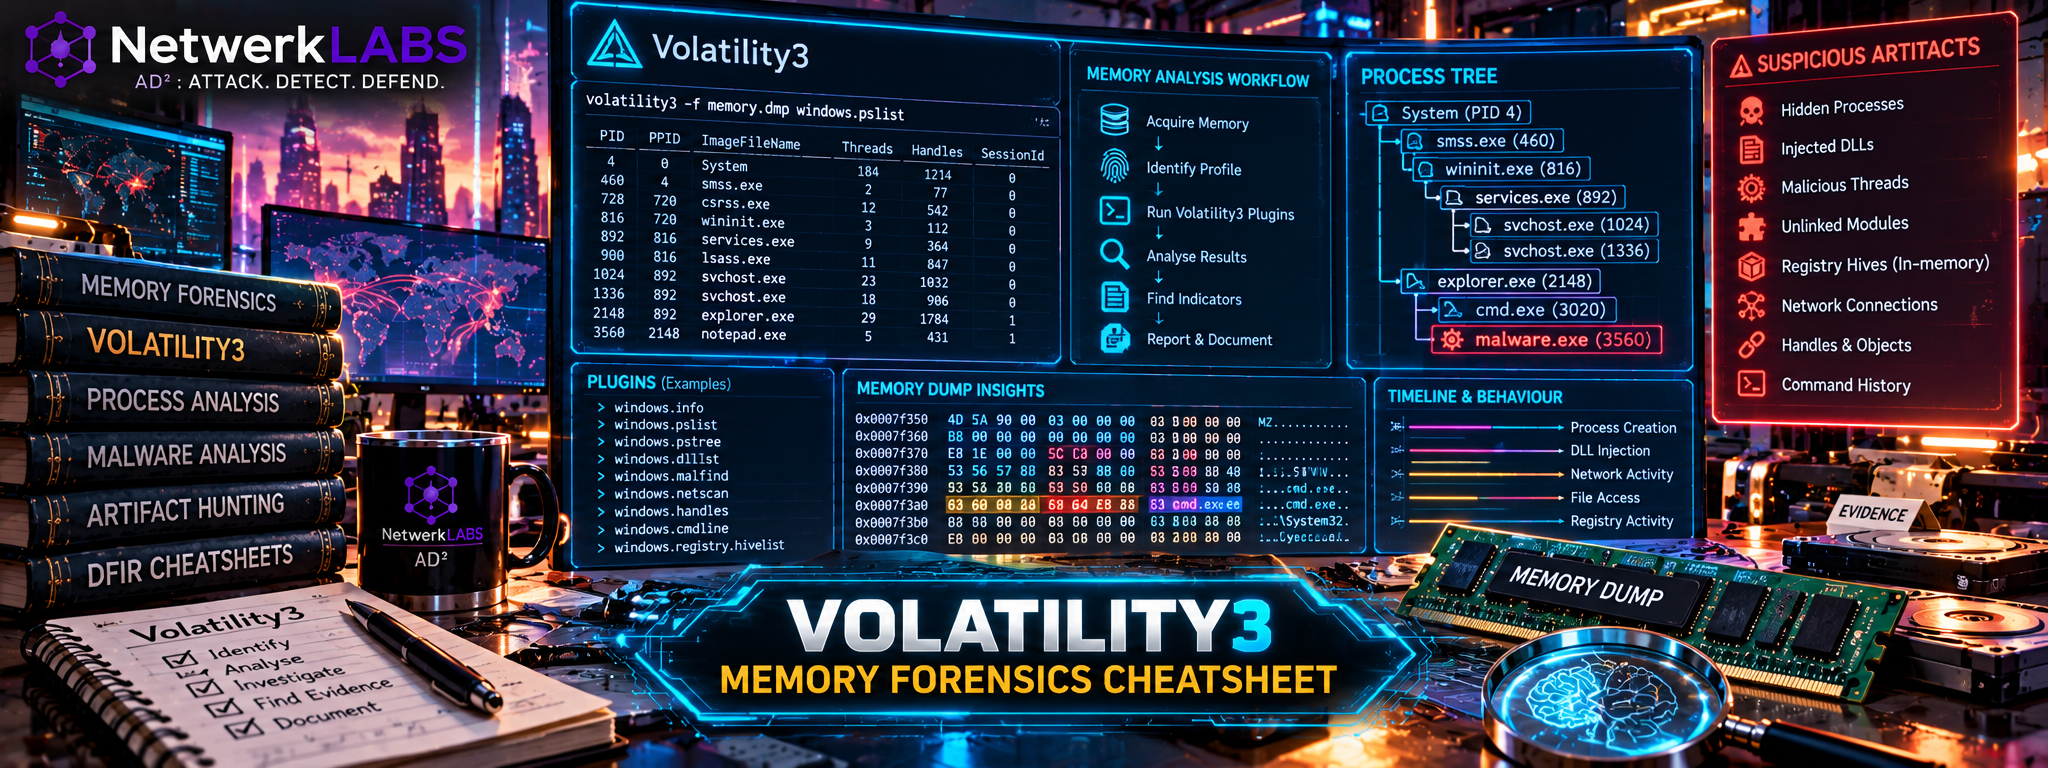
Volatility3: Memory Forensics Cheatsheet

VOLATILITY 3 Memory Forensics Investigation Cheatsheet DFIR | Detection Engineering | Threat Hunting | CyberDefenders Labs 01 │ SETUP & FUNDAMENTALS # Install via pip pip install volatility3 # Or clone from GitHub git clone https://github.com/volatilityfoundation/volatility3.git…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
Posted inDetection Engineering DETECT Purple Teaming

Misbehaving binaries: Hunting LOLBinsĀ 

šŸ•µļøā€ā™‚ļø Detection Engineering: Catching jsc.exe Abuse (T1127) 🟣 Technique: Trusted Developer Utilities Proxy Execution (MITRE ATT&CK T1127)šŸ”µ Tool abused: jsc.exe, the Microsoft JScript .NET compiler🟢 Stack: Atomic Red Team āžœ Sysmon āžœ Elastic Agent āžœ Elastic…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
Posted inDETECT MITRE ATT&CK Purple Teaming

Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: I]

Getting More Out of MITRE ATT&CK in Threat Modelling MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) is an openly available knowledge base describing how cyber adversaries behave. The MITRE Corporation maintains it. Organisations use it…
Continue Reading
Posted by Avatar photo Bharath Narayanasamy
MSFVenom Cheatsheet for Reverse_Shell Payloads
Posted inRED TEAM

MSFVenom Cheatsheet for Reverse_Shell Payloads

Non-Meterpreter We can execute the msfvenom --list-payloads command to see a brief description about all of the payloads msfvenom can offer, if we want to know specific information about the payload, executing a msfvenom -p payload…
Read More
Posted by Avatar photo Bharath Narayanasamy Tags: Exploitation, payloads, msfvenom

Posts pagination

Previous page 1 … 18 19 20

Recent Posts

  • Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: II]
  • 8 LOLBins Every Threat Hunter Should Know
  • Living Off the Land (LOTL) Resources
  • Volatility3: Memory Forensics Cheatsheet
  • Misbehaving binaries: Hunting LOLBinsĀ 

Categories

AD AD attacks Atomic RED brute-force c2 caldera CISO dfir Elastic hydra linux NIST red-team SIEM splunk Threat Intel threat_detection vulnhub wazuh wireshark

You May Have Missed
Posted inThreat Hunting DETECT MITRE ATT&CK

Using MITRE ATT&CK Navigator to Strengthen Threat Modelling [PART: II]

Posted by Avatar photo Bharath Narayanasamy
Posted inThreat Hunting DETECT Detection Engineering

8 LOLBins Every Threat Hunter Should Know

Posted by Avatar photo Bharath Narayanasamy
Posted inATTACK Detection Engineering DETECT

Living Off the Land (LOTL) Resources

Posted by Avatar photo Bharath Narayanasamy
Posted inDFIR DETECT

Volatility3: Memory Forensics Cheatsheet

Posted by Avatar photo Bharath Narayanasamy
Copyright 2026 — NetwerkLABS. Powered by TekGenX Consulting. All rights reserved.
Scroll to Top

Powered by
Necessary cookies enable essential site features like secure log-ins and consent preference adjustments. They do not store personal data.
None
Functional cookies support features like content sharing on social media, collecting feedback, and enabling third-party tools.
None
Analytical cookies track visitor interactions, providing insights on metrics like visitor count, bounce rate, and traffic sources.
None
Advertisement cookies deliver personalized ads based on your previous visits and analyze the effectiveness of ad campaigns.
None
Unclassified cookies are cookies that we are in the process of classifying, together with the providers of individual cookies.
None
Powered by